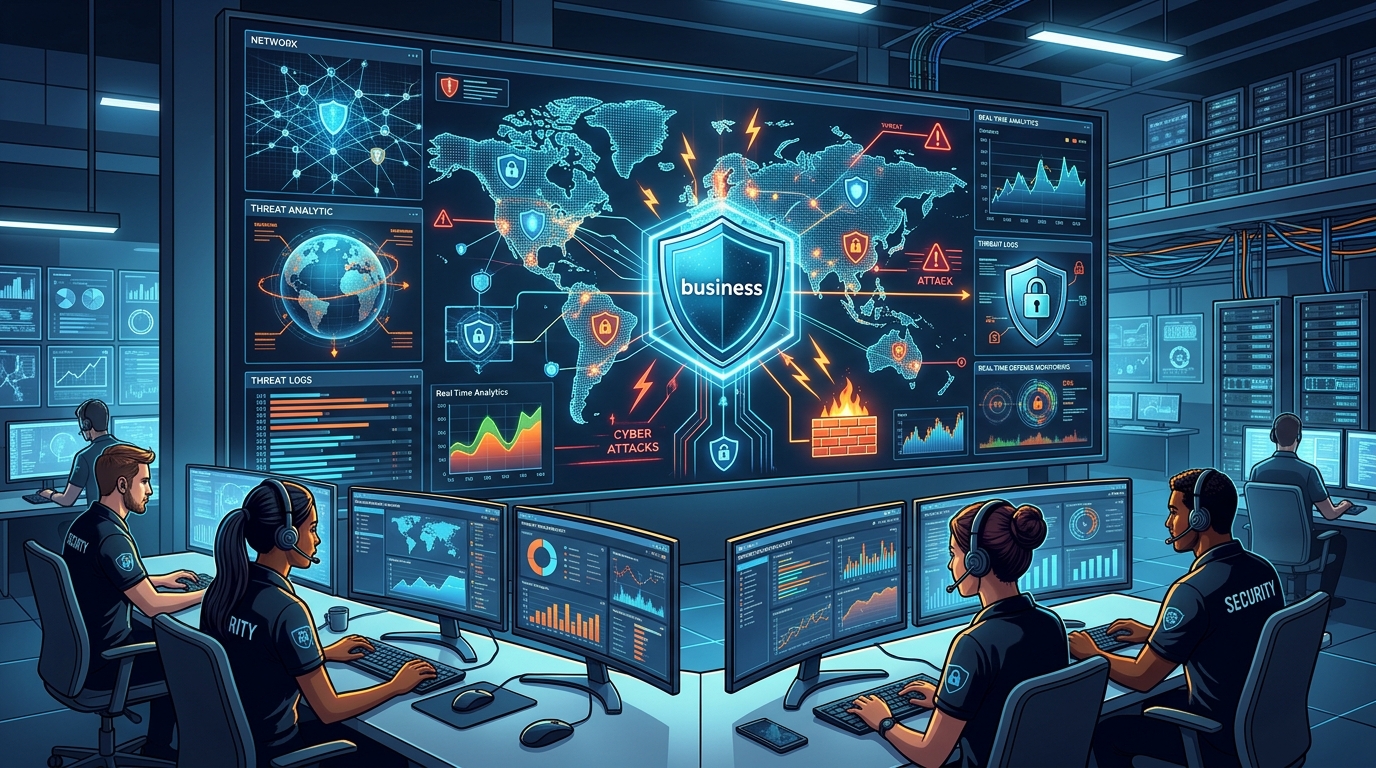
A Security Operations Center acts as the central command post for an organization’s cybersecurity infrastructure. In today’s digital landscape, threats emerge at a lightning-fast pace. Consequently, businesses must adopt proactive measures to protect their sensitive data. Understanding what is a Security Operations Center (SOC) is the first step toward achieving total digital resilience. At SSL UK, we emphasize the importance of continuous vigilance to stay ahead of sophisticated cybercriminals.
What is a Security Operations Center (SOC)?
A Security Operations Center is a centralized unit that deals with security issues on an organizational and technical level. It consists of a dedicated team of experts who monitor, detect, and respond to cyber threats. The primary goal is to identify vulnerabilities before attackers can exploit them. Therefore, the SOC serves as the first line of defense in a complex digital environment. It is not just about technology; it is about the synergy between people, processes, and tools.
The team within a SOC uses advanced technologies to oversee the entire IT infrastructure. This includes networks, servers, endpoints, and databases. Moreover, they analyze traffic patterns to spot any unusual activity. If they detect a potential breach, they act immediately to mitigate the impact. This proactive stance is what separates a modern business from a vulnerable one.
The Core Functions of a Security Operations Center
A Security Operations Center performs several critical tasks to maintain a high level of security. First, the team maintains an inventory of all digital assets. You cannot protect what you do not know exists. Subsequently, they implement monitoring tools to gain full visibility into the network. This constant oversight ensures that no suspicious packet goes unnoticed. Additionally, they manage logs and analyze data to improve future security strategies.
Another vital function is incident response. When a threat is identified, the SOC team follows a strict protocol. They isolate the affected systems to prevent the spread of malware. Furthermore, they perform forensic analysis to understand how the attacker gained access. This information is invaluable for strengthening the perimeter against future attempts. By doing so, they minimize downtime and protect the company’s reputation.
Real-Time Monitoring and Threat Detection
Real-time monitoring is perhaps the most visible aspect of a SOC. The team uses Security Information and Event Management (SIEM) systems to aggregate data from across the organization. These systems flag anomalies that might indicate an ongoing attack. For example, multiple failed login attempts from a foreign IP address will trigger an alert. The analysts then investigate these alerts to determine their severity.
Because hackers never sleep, a SOC 24/7 UK service is highly beneficial for local enterprises. Cyberattacks can happen at any hour, often during holidays or weekends when staff is minimal. Therefore, having a team that operates around the clock ensures that your defense is never down. This continuous operation provides peace of mind for business owners and stakeholders alike.
Why Your Business Needs a SOC 24/7 UK Service
Operating a security team during standard office hours is no longer sufficient. Most modern threats are automated and can strike at any moment. This is why a SOC 24/7 UK model has become the gold standard for protection. It ensures that regardless of the time zone or the hour, expert eyes are watching your data. Consequently, the window of opportunity for an attacker is significantly reduced.
In addition to 24/7 coverage, a UK-based SOC offers geographical advantages. They understand the local threat landscape and specific regulatory requirements like GDPR. Furthermore, communication is easier when your security partner shares your language and time zone. This local expertise helps in tailoring security policies that fit the specific needs of UK businesses. Investing in a local SOC means investing in a team that truly understands your environment.
The Critical Roles within a SOC Team
A successful Security Operations Center relies on diverse expertise. At the entry level, Tier 1 Analysts monitor alerts and perform initial triaging. They filter out the noise and identify real threats. If a threat is complex, they escalate it to Tier 2 Analysts. These specialists perform deep-dive investigations and handle the actual incident response. They are the tactical experts who neutralize the attackers.
Higher up, Tier 3 Analysts or Threat Hunters proactively search for hidden threats within the network. They do not wait for an alert to pop up. Instead, they use their expertise to find weaknesses that automated tools might miss. Finally, the SOC Manager oversees the entire operation, ensuring that the team follows best practices. This hierarchical structure ensures that every incident receives the appropriate level of attention and expertise.
The Technology Behind an Information Security Operations Center
Technology plays a massive role in the effectiveness of a SOC. According to the definition of an information security operations center, it requires a robust stack of tools. This includes firewalls, intrusion detection systems (IDS), and endpoint detection and response (EDR) software. These tools provide the data that analysts need to make informed decisions.
Artificial Intelligence (AI) and Machine Learning (ML) are also becoming integral. These technologies can process vast amounts of data much faster than any human. They can identify patterns of behavior that indicate a breach is imminent. However, technology alone is not a silver bullet. It requires skilled professionals to interpret the results and take action. The combination of human intelligence and machine speed creates a formidable barrier for cybercriminals.
Compliance and Risk Management
Beyond threat detection, a SOC helps businesses maintain compliance with industry standards. Many regulations require organizations to have continuous monitoring and incident response plans in place. A Security Operations Center provides the documentation and audit trails necessary to prove compliance. This is especially important for sectors like finance, healthcare, and law. By maintaining high security standards, you not only avoid fines but also build trust with your clients.
Risk management is another area where the SOC excels. By identifying vulnerabilities early, the team helps the business prioritize its security investments. They provide data-driven insights into which areas are most at risk. Therefore, management can allocate resources more effectively. This strategic approach ensures that the security budget is spent where it will have the most significant impact.
Conclusion: Securing Your Future with SSL UK
In conclusion, the question of “what is a Security Operations Center (SOC)” leads to a single answer: it is an essential component of modern business survival. As cyber threats become more sophisticated, relying on traditional antivirus software is no longer enough. You need a dedicated team, advanced technology, and a 24/7 vigilance strategy. A SOC 24/7 UK service offers the best protection for organizations looking to thrive in a digital-first world.
At SSL UK, we specialize in providing top-tier security solutions tailored to your unique needs. Our team of experts is dedicated to protecting your assets and ensuring your business remains resilient against any attack. Do not wait for a breach to happen before taking action. Contact us today to learn how we can help you build a robust Security Operations Center and safeguard your digital future. Protect your data, protect your reputation, and protect your peace of mind with our expert services.